Journal
15 min read
UAE PDPL Compliance Guide for Websites (2026)
What UAE PDPL actually requires of websites and software: federal law vs DIFC/ADGM, consent, data-subject rights, breach rules, and how to build compliance in.
By NxFold
Updated 4 Sept 2026
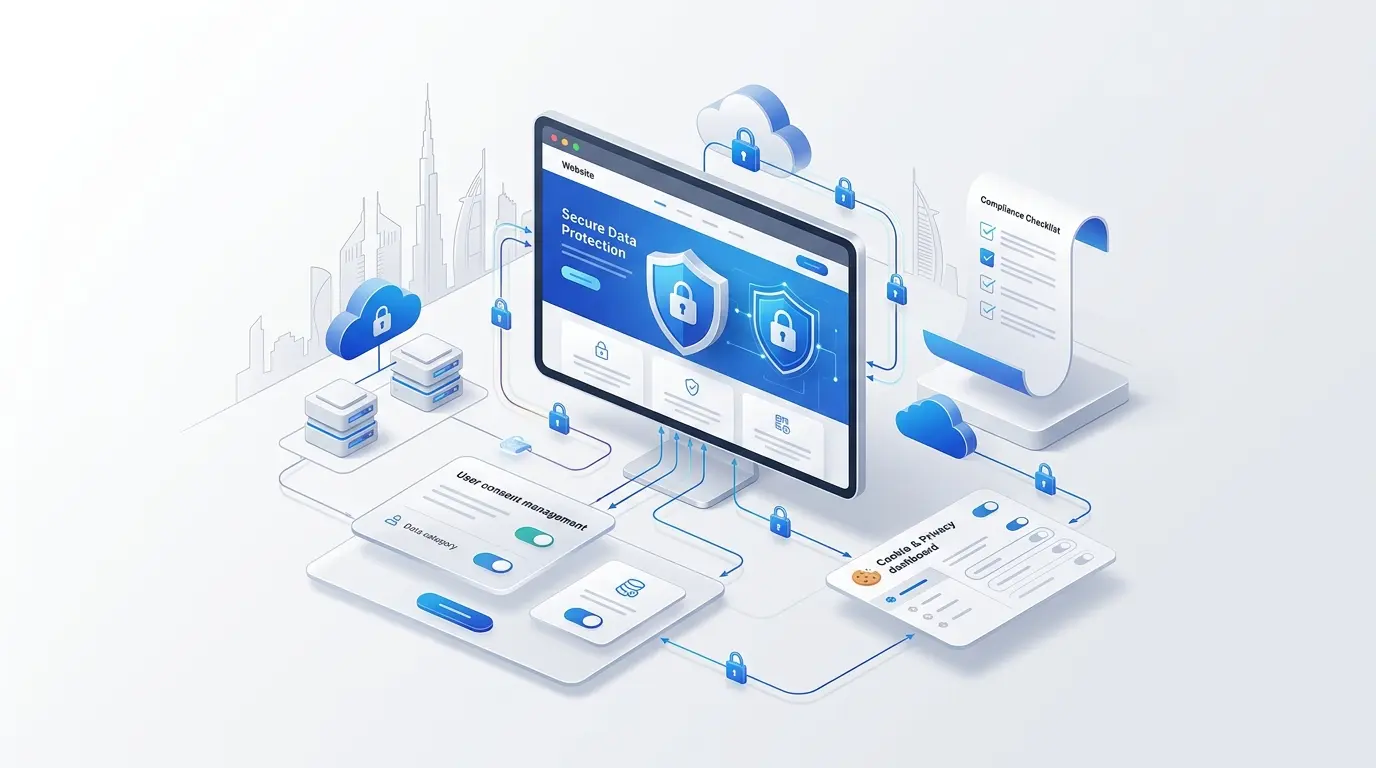
A lot of founders treat data protection compliance as a checkbox: paste a privacy policy template into the footer, add a cookie banner, done. In the UAE, that instinct runs into a more fragmented reality than most people expect — a federal law that applies across the mainland, plus two separate free-zone regimes (DIFC and ADGM) with their own rules, plus sector-specific rules for finance and healthcare that sit on top of all of it. Building software without understanding which layer applies to your business is how founders end up compliant on paper and exposed in practice.
This guide covers what the UAE's Personal Data Protection Law (Federal Decree-Law No. 45 of 2021, "PDPL") actually requires of a typical business building or operating a website, app, or SaaS product, how it differs from the free-zone regimes, and — more usefully — what to actually build into software from day one so compliance isn't a rushed retrofit six months after launch.
The Short Answer
If your business operates on the UAE mainland, the federal PDPL applies to you, and it requires: a lawful basis for processing personal data (usually consent, but not always), the ability to fulfill data subject requests — access, correction, deletion, portability — within 30 days, appropriate technical security measures, and prompt breach notification to the UAE Data Office. If your business is registered in DIFC or ADGM, a separate, more GDPR-like data protection regime applies instead of (not in addition to) the federal law for data processed within that free zone. Sensitive data — health, biometric, religious, political, criminal — needs explicit consent almost always, with a much higher bar than general personal data.
The single most common mistake is treating "privacy policy exists" as equivalent to "PDPL compliant." A privacy policy is a disclosure document. Compliance is an operational capability — can your system actually produce, correct, or delete a specific person's data on request within 30 days? Most teams find out the answer is no only when the first request arrives.
The Three-Layer Reality: Federal PDPL, DIFC, and ADGM
The UAE doesn't have one data protection law — it has three parallel regimes, and which one applies depends on where your business is legally established, not where your customers are.
Federal PDPL applies to the UAE mainland and to any free zones that haven't adopted their own regime. This is the law that applies to most standard mainland-licensed businesses, e-commerce sites, and SaaS products.
DIFC Data Protection Law applies to entities established in the Dubai International Financial Centre. It is closely modeled on the EU's GDPR and is generally considered the stricter of the UAE's regimes, with its own independent regulator (the DIFC Commissioner of Data Protection).
ADGM Data Protection Regulations apply to entities established in Abu Dhabi Global Market, and are also GDPR-influenced, with their own regulator.
If a business operates across more than one of these — for example, a mainland-licensed operating company with a DIFC-registered holding entity, or a SaaS product serving customers whose data is processed by a DIFC-based subsidiary — the correct regime to apply depends on which entity is legally the data controller for a given processing activity. This is a genuine legal-structuring question, not a development one, and it's worth resolving with counsel before choosing where to license a new venture, not after building the product around the wrong assumption.
What Counts as "Personal Data" (and What's "Sensitive")
Personal data under PDPL is defined broadly: any information that identifies a natural person, directly or indirectly — name, email, phone number, ID number, IP address, device identifiers, and location data all qualify. This is a wider net than many founders expect; an analytics cookie capturing an IP address is processing personal data under PDPL, even without a name attached.
Sensitive personal data is a narrower, higher-risk category: family or racial origin, political or philosophical opinions, religious beliefs, criminal records, and biometric data (including facial images used for identification). Processing sensitive data requires a materially higher standard of consent — explicit, specific, and freely given, not bundled into a general terms-of-service checkbox.
This distinction matters directly for a lot of software builds in this market: a facial-recognition check-in feature, a health questionnaire in a wellness app, or a religious-affiliation field in a form all cross into sensitive-data territory and need their own explicit consent flow, separate from a general "I agree to the privacy policy" checkbox.
Lawful Basis: When You Actually Need Consent
Consent is the basis most founders reach for by default, but PDPL — like most modern data protection laws — recognizes several other lawful bases that often fit better and create less operational overhead: processing necessary to perform a contract with the individual (fulfilling an order, providing a subscribed service), compliance with another UAE law, protecting the vital interests of the data subject, and legitimate business interests that don't override the individual's own rights.
The practical implication: a SaaS product processing a customer's account data to actually deliver the service doesn't necessarily need a separate consent checkbox for that core processing — it's covered under contractual necessity. Where consent genuinely is required — marketing emails, third-party data sharing, sensitive data processing, cookies used for tracking beyond strict necessity — it needs to be specific, informed, and as easy to withdraw as it was to give. Pre-ticked boxes and bundled "by using this site you agree to everything" consent don't meet that bar.
Data Subject Rights You Must Be Able to Fulfill
PDPL grants individuals five core rights, and — this is the part that actually requires engineering work, not just legal drafting — controllers must be able to act on them within 30 days of a request (extendable in complex cases):
| Right | What it requires operationally |
|---|---|
| Access | Produce a copy of all personal data held about the individual |
| Rectification | Correct inaccurate or incomplete data on request |
| Erasure | Delete the individual's data once the lawful basis for holding it ends |
| Portability | Export the individual's data in a structured, machine-readable format |
| Objection | Stop processing based on legitimate interest or direct marketing grounds |
For a typical custom software build, this means: personal data needs to be locatable across every system it touches (the app database, the email marketing tool, the analytics platform, the support ticketing system, backups), not just the primary database. Products built with data scattered across a dozen disconnected third-party tools with no central inventory routinely miss the 30-day window simply because nobody can find all of it in time — not because anyone refused to comply.
Do You Need a Data Protection Officer?
Not automatically. PDPL doesn't impose a blanket DPO requirement the way GDPR effectively does for many organizations. A formal DPO appointment becomes necessary when processing involves systematic, large-scale processing of sensitive data, or high-risk processing using new technologies (large-scale biometric matching, extensive automated profiling, and similar). Most standard e-commerce sites, service businesses, and SaaS products with typical customer data don't cross that threshold and don't need a formally appointed DPO — though designating someone internally as responsible for data protection questions is good practice regardless of whether it's legally mandatory.
Cross-Border Transfers and Data Localization
This is the area where founders using international cloud infrastructure — AWS, Cloudflare, Google Cloud — most often have unanswered questions, and the honest answer is: it depends heavily on sector, and the general-purpose rule is less restrictive than the sector-specific ones.
For most standard businesses, PDPL doesn't require blanket in-country storage of all personal data — international cloud hosting is generally workable, subject to the Data Office's forthcoming rules on adequacy of destination jurisdictions. Where mandatory local storage genuinely applies is sector-specific: financial institutions must generally keep customer and payment transaction data within the UAE under Central Bank rules (the same regulatory backdrop covered in our payment gateway integration guide), healthcare providers face local-storage requirements for diagnostic and medical records under health-authority rules, and certain government-adjacent data categories have their own restrictions.
The practical guidance for a typical SaaS or e-commerce build: general customer account data, analytics, and marketing data can usually sit on standard international cloud infrastructure. Payment transaction data, health records, and biometric data need a sector-specific check before you assume the same rule applies — this is exactly the kind of detail worth confirming with counsel at the architecture stage, not after a system is already built around the wrong assumption.
Breach Notification: What Actually Happens
When a breach occurs, PDPL requires notifying the UAE Data Office, with an increasingly tight timeline expectation as implementing regulations mature — treat prompt, near-immediate notification as the safe assumption rather than waiting to see how much time you can take. Where a breach poses a genuine risk to affected individuals' rights, they must be notified directly as well. Sector regulators add their own layer on top: financial institutions must separately notify the Central Bank of significant breaches affecting customers.
The operational lesson mirrors the data-subject-rights point above: if a breach happens, you need to be able to quickly identify what data was affected and which individuals it belongs to. That's a data-inventory and logging problem to solve before an incident, not during one.
What Non-Compliance Actually Costs
Penalty figures reported for PDPL violations run from the tens of thousands of dirhams for lesser violations up to several million dirhams for serious ones — processing sensitive data without a lawful basis, unlawful cross-border transfers, or failing to notify a breach sit at the high end of that range, with criminal liability under separate UAE cybercrime and penal statutes for the most serious cases (unauthorized disclosure, malicious misuse of data). The exact tiers depend on implementing regulations issued under the law, which continue to be refined — the safe planning assumption is that enforcement activity is increasing, not that early leniency will continue indefinitely.
This is not the kind of risk to price against "how likely is an audit" — the more relevant comparison is the operational cost of retrofitting compliance into a system that wasn't built for it versus the marginal cost of building it in from the start.
Building Compliance Into Software from Day One
The teams that handle this well treat data protection as an architecture decision, not a legal afterthought bolted onto a finished product:
Data inventory as a first-class concern. Know, for every category of personal data your system touches, where it lives, why you have it, and how long you keep it. This is the single highest-leverage piece of groundwork — every other requirement (access requests, deletion, breach response) depends on being able to answer this quickly.
Deletion and export as real features, not manual processes. Build an admin-accessible (or even self-service) capability to export and permanently delete a given user's data across every system it touches — including backups and third-party tools — rather than relying on someone manually hunting through databases when a request arrives. This is directly relevant to the tenant data isolation patterns discussed in our multi-tenant SaaS architecture guide — a clean per-tenant data boundary makes "delete everything belonging to this customer" a solvable engineering problem instead of a database archaeology project.
Consent as structured data, not a checkbox in a form. Store what a user consented to, when, and under what version of the policy — as queryable records, not just a boolean flag. This makes it possible to prove compliance later and to honor withdrawal requests precisely (stopping only what was actually consented to, not everything).
Encryption and access controls proportionate to sensitivity. General account data and sensitive data (biometric, health, payment) warrant different levels of protection — encryption at rest, field-level access restrictions, and audit logging matter most where the data itself is highest-risk.
Retention limits enforced in code, not just policy. If a privacy policy says data is deleted after a certain period, that should be an automated job, not a manual process someone forgets to run.
Common Mistakes We See
Treating the privacy policy as the compliance deliverable. A well-written policy that describes capabilities the system doesn't actually have (like fulfilling a deletion request in 30 days) is arguably worse than no policy, since it creates a documented gap between claimed and actual practice.
Assuming international cloud hosting is automatically fine — or automatically a problem. Both extremes are wrong. The correct answer depends on data category and sector, and it's worth resolving explicitly rather than guessing in either direction.
Bundling consent into one giant checkbox. "I agree to the terms, privacy policy, marketing emails, and cookie tracking" in a single checkbox doesn't meet the specific-and-informed consent standard for anything beyond strictly necessary processing.
No internal owner for data protection questions. Even without a legal DPO requirement, someone on the team should own the question "can we fulfill a data subject request right now" — otherwise the first real request becomes a fire drill.
Ignoring free-zone jurisdiction questions at incorporation. Choosing between mainland, DIFC, or ADGM licensing has real data protection consequences that are much cheaper to get right at company formation than to restructure around later.
PDPL vs. GDPR: A Quick Comparison
| UAE PDPL | EU GDPR | |
|---|---|---|
| DPO requirement | Only for high-risk/large-scale sensitive processing | Broad requirement for many public bodies and large-scale processors |
| Data subject response window | 30 days (extendable) | 1 month (extendable, same practical window) |
| Maximum penalties | Reported up to several million AED for serious violations | Up to €20 million or 4% of global annual revenue |
| Free-zone variance | DIFC and ADGM have separate, GDPR-like regimes | Single regime across all EU member states |
| Data localization | Sector-specific (finance, health); general data more flexible | No blanket localization requirement, but strict rules on transfers outside the EU |
Frequently Asked Questions
Does my business need to comply with PDPL if my customers are outside the UAE? If your business is established in the UAE mainland and you process personal data as part of that operation, PDPL applies to your processing activities regardless of where individual customers are located, though the analysis can get more nuanced with fully international customer bases — worth a specific legal check for cross-border business models.
Is a cookie consent banner legally required? PDPL doesn't spell out cookie-specific rules as explicitly as the EU's ePrivacy rules do, but any cookie or tracking technology that processes personal data (including IP addresses and device identifiers) needs a lawful basis, and where that basis is consent, it needs to be genuine, specific, opt-in consent — not implied by continued browsing.
Do I need to appoint a Data Protection Officer? Only if your processing involves large-scale sensitive data handling or high-risk automated processing. Most standard e-commerce and SaaS businesses don't cross that threshold, though designating an internal owner for data protection is good practice regardless.
Can I host UAE customer data on AWS, Cloudflare, or Google Cloud? For most general business data, yes — international cloud hosting is generally workable. Payment transaction data, health records, and certain other sector-specific categories have stricter localization expectations and should be checked against sector rules before assuming standard cloud hosting applies.
What happens if we can't fulfill a data subject request within 30 days? The law allows an extension in genuinely complex cases, but that's not a substitute for having the operational capability to respond at all. Businesses that can't locate a specific individual's data across their systems within a reasonable window have a real compliance gap, not just a documentation one.
How is this different from just having a privacy policy? A privacy policy discloses what you do. Compliance means you can actually do what the policy says — produce, correct, delete, or export a specific person's data on request, notify a breach promptly, and process sensitive data only with genuine explicit consent. The policy is the description; the operational capability is the compliance.
Does PDPL apply the same way in DIFC or ADGM? No — DIFC and ADGM each have their own separate data protection regime, closely modeled on GDPR, administered by their own regulators. If your entity is established in one of those free zones, that regime applies instead of the federal PDPL for data processed within it.
What's the single highest-priority thing to get right first? Data inventory — knowing exactly what personal data your systems hold, where, and why. Nearly every other obligation (access requests, deletion, breach response, retention limits) depends on being able to answer that quickly, and it's the piece most software builds skip until it's already a problem.
The Bottom Line
PDPL compliance for a typical UAE business isn't primarily a legal-drafting exercise — it's an operational and architectural one. The businesses that handle it well build data inventory, deletion, export, and consent tracking into the software itself from the start, rather than trusting a privacy policy to paper over gaps a real data-subject request would expose. The jurisdictional layer (federal PDPL vs. DIFC vs. ADGM) is worth resolving at the legal-structuring stage, and the sector-specific localization rules (finance, health) are worth checking explicitly rather than assuming either extreme.
If you're building custom software and want data protection handled as part of the architecture rather than bolted on afterward, get in touch — we'll help you scope the right data model, consent handling, and compliance posture from the first sprint.
Have a project in mind?
Ideas to put into practice.
Turn what you have learned into a clearer plan for your website or product. Tell us what you want to build.
Start your project